Advisory · Security Assessments
Know where you stand before an attacker, insurer, or auditor tells you.
An independent assessment of your Microsoft 365 tenant, network, devices, and vendors, delivered as a prioritized, plain-language plan that leadership can act on.
Why it matters
Small and mid-size organizations are prime targets.
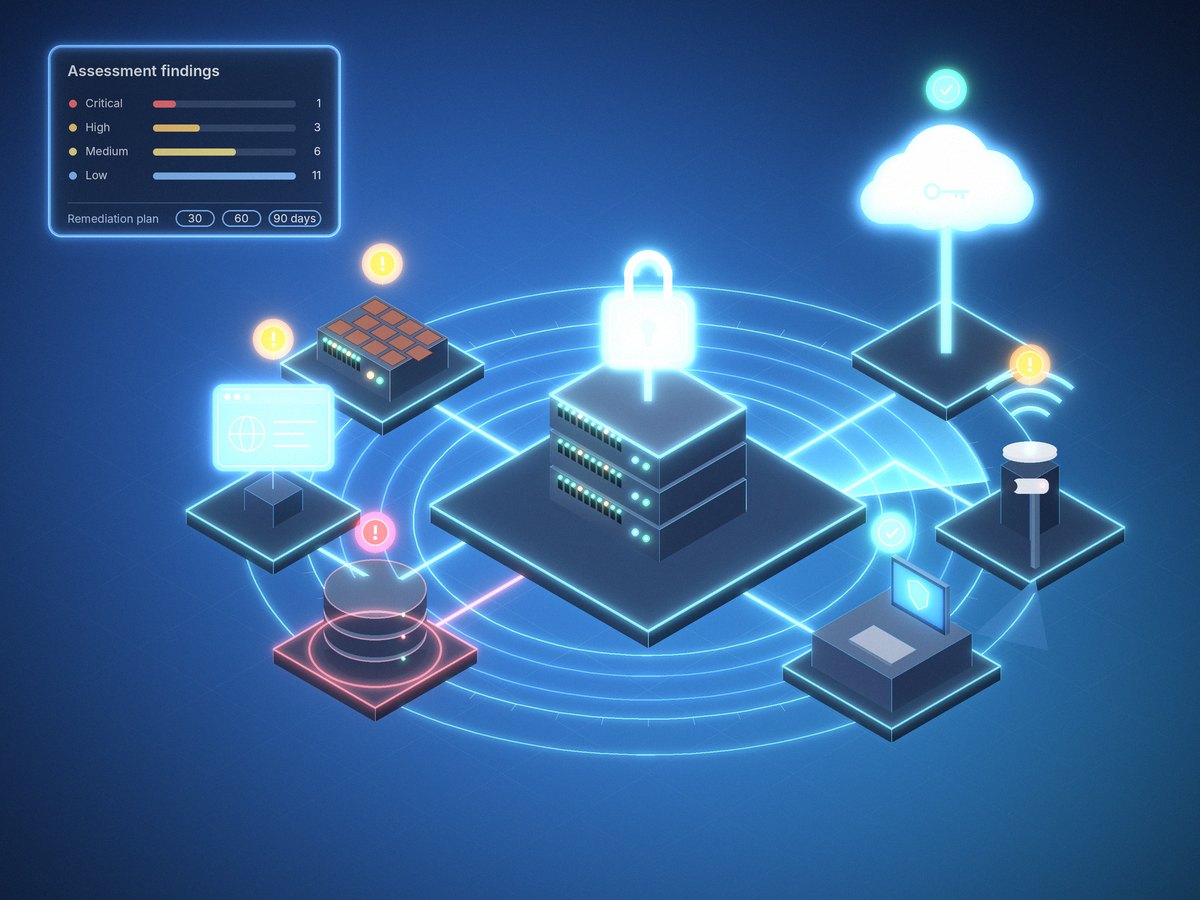
Attackers target organizations with valuable data and thin IT resources: health centers, nonprofits, and growing businesses. Most breaches start with something fixable, such as a missing multifactor setting, an unpatched plugin, or an overlooked vendor account.
An assessment finds those gaps first, ranks them by business risk, and gives you a realistic plan and budget to close them.
What we assess
A complete view across cloud, network, and physical security.
Microsoft 365 and identity
Multifactor authentication, Conditional Access, admin roles, sharing settings, and Secure Score.
Network and firewall
Firewall rules, segmentation, remote access, and firmware across your sites.
Wireless and physical security
Wi-Fi configuration, guest isolation, cameras, and door access controls.
Endpoints and patching
Device protection, encryption, update status, and local admin rights.
Backup and recovery
Whether backups exist, are protected from ransomware, and can actually be restored.
Website and vendor risk
Public websites, hosting accounts, and third parties with access to your systems.
What you receive
Findings leadership can understand and act on.
- Executive summary in plain language
- Findings ranked by business risk
- Remediation roadmap with estimated costs
- Documentation to support cyber insurance and audits
- Leadership briefing to walk through results
- 01
Scope
Agree on sites, systems, and any compliance requirements.
- 02
Discover
Review configurations, interview staff, and inspect sites.
- 03
Analyze
Rank each finding by likelihood and business impact.
- 04
Report and brief
Present results and the remediation plan to leadership.